Three pillars of cybersecurity best practices
The IBM and Ponemon Institute’s Cost of a Data Breach Report 2024 reported that the average cost of a data breach went up 10% to $4.88 million for all industries. By implementing comprehensive cybersecurity best practices, businesses can significantly reduce their risk exposure and build resilience against cyber threats.
Adopting cybersecurity best practices is a strategic business decision that will mitigate cyber risk and strengthen cyber resilience. From establishing a robust security culture and implementing strong access controls to ensuring network security and developing incident response plans, each of these practices will provide more security to your business from cyber threats. A proactive defense is a competitive advantage.
According to the UK’s National Cyber Security Center, there are three key pillars to cybersecurity that large organizations should consider:
- Understanding your organization’s risks
- Implementing appropriate mitigations
- Preparing for cyber incidents
The NCSC then breaks down the pillars into ten components. There isn’t one pillar that is more important than the other, rather they work in a cycle of improvement.
Understanding your risks enables you to identify appropriate mitigations that lead to more effective preparations in the event of a cyber incident.
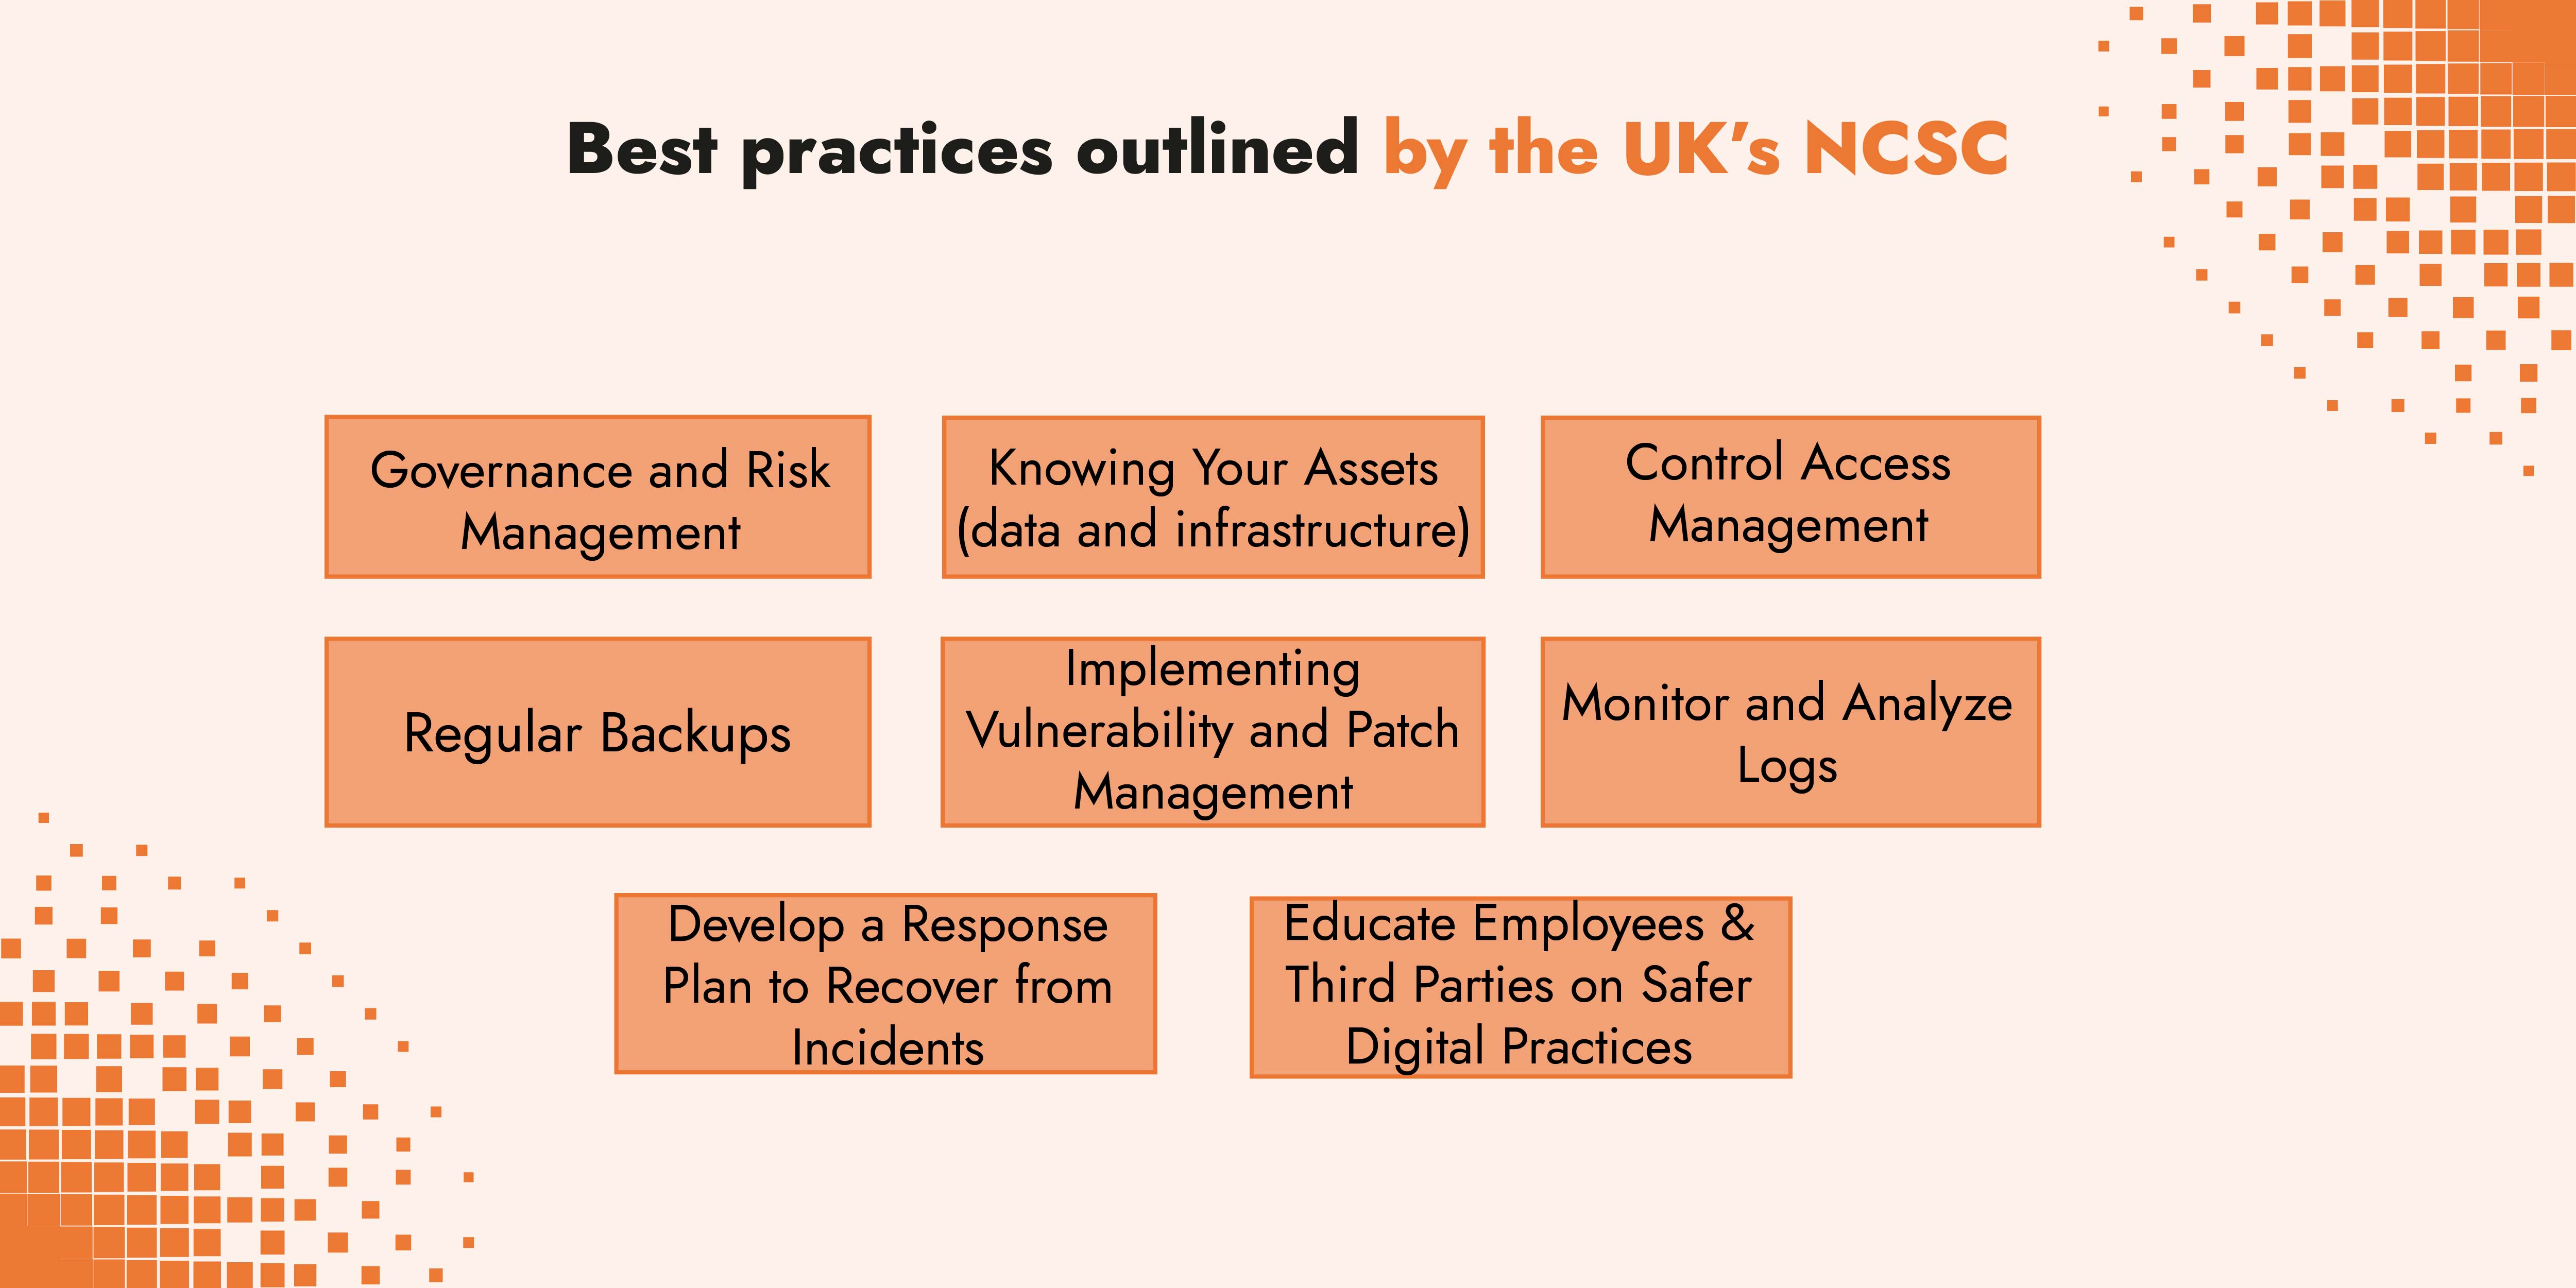
In this article, we will explore the following best practices that fall under the three pillars outlined by the UK’s NCSC:
- Governance and Risk Management
- Knowing Your Assets (data and infrastructure)
- Control Access Management
- Regular Backups
- Implementing Vulnerability and Patch Management
- Monitor and Analyze Logs
- Develop a Response Plan to Recover from Incidents
- Educate Employees and Third Parties on Safer Digital Practices
Understand your organization’s risks
Governance and risk management
Effective cybersecurity begins with governance and risk management. This belongs to the NCSC’s pillar Understanding your organization’s risks. A company with a comprehensive governance and risk management framework will be able to identify and address enterprise-wide cyber risks more effectively. Cybersecurity is not only an issue for the IT department. The digital transformation has made all business processes more vulnerable to threat actors.
CISA, the Cyber Defense Agency in the US, defines cybersecurity governance as “a comprehensive cybersecurity strategy that integrates with organizational operations and prevents the interruption of activities due to cyber threats or attacks”. This includes mitigation plans, decision-making hierarchies, accountability frameworks, and understanding risks as they relate to business objectives.
Cyber risk management is a critical part of governance and allows business leadership to understand risks related to digital processes, critical assets and systems, and third parties. According to ISO 27005 and other risk management frameworks, risk management includes risk assessment, risk treatment and risk monitoring. These three sub-categories are necessary to identify assets, scope risks, measure control efficacy and make recommendations. A data-driven approach to risk management will provide defensible data to critical stakeholders for effective decision-making.
Implement risk mitigations
Maintaining the CIA triad – confidentiality, integrity, and availability – is the objective of the infosec team. There are many controls that can be implemented to reduce the risk of a threat actor gaining access to your data. Below are a selection of
Strong credential management
Credential management is the process of creating, storing, managing and protecting digital credentials by only allowing authorized users to access sensitive information and resources.
Zero Trust is a security framework that limits system or information access based on a user's role, and continuously verifies credentials before granting access to a user. Zero Trust also includes continuous control of who has access to data and denying access to users who no longer require access to perform their job.
MFA or multi-factor authentication is a critical step to improving credential management. MFA requires users to provide two or more verification factors to access a network, system or account. MFA used a combination of the three ways to verify a person’s identity:
Something you know – this can be a password or PIN you have memorized
Something you have – this is using a smartphone or other device
Something you are – this can include biometric data like a fingerprint or facial recognition
Backup and recovery strategy
Both businesses and individuals can protect their data by implementing a backup and recovery strategy. Backup and recovery ensure that data and systems can be restored in the event of cyberattacks, such as ransomware, data breaches, or system failures, increasing cyber resilience against these threats.
- Duplicate your data backups: you can follow the 3-2-1 strategy, that is one primary copy and two backups.
- Use multiple storage types: It’s best practice to store each backup in separate locations, for example, one backup in the cloud and one on local storage and not connected to your network.
- Frequent automatic backups: Regular backups help to minimize data loss in the case of ransomware.
- Encrypt your data: Encrypted backups prevent unauthorized access and potential breaches of sensitive data.
- Test your backup and recovery procedure: Regularly test the restoration process to ensure backups can be successfully retrieved and that critical systems can be brought back online. This ensures data hasn’t been corrupted or altered.